Hero Image

Securing the Software Supply Chain with SLSA & Attestation

November 19

Sign Up Now

Modern software delivery introduces complex risks across every stage of the development lifecycle. Join Adfinis expert Lukas Grossar to discover how to move beyond traditional, weak trust mechanisms, like basic checksums or PGP signatures, and implement end-to-end cryptographic verification across your pipelines.

Key Takeaways
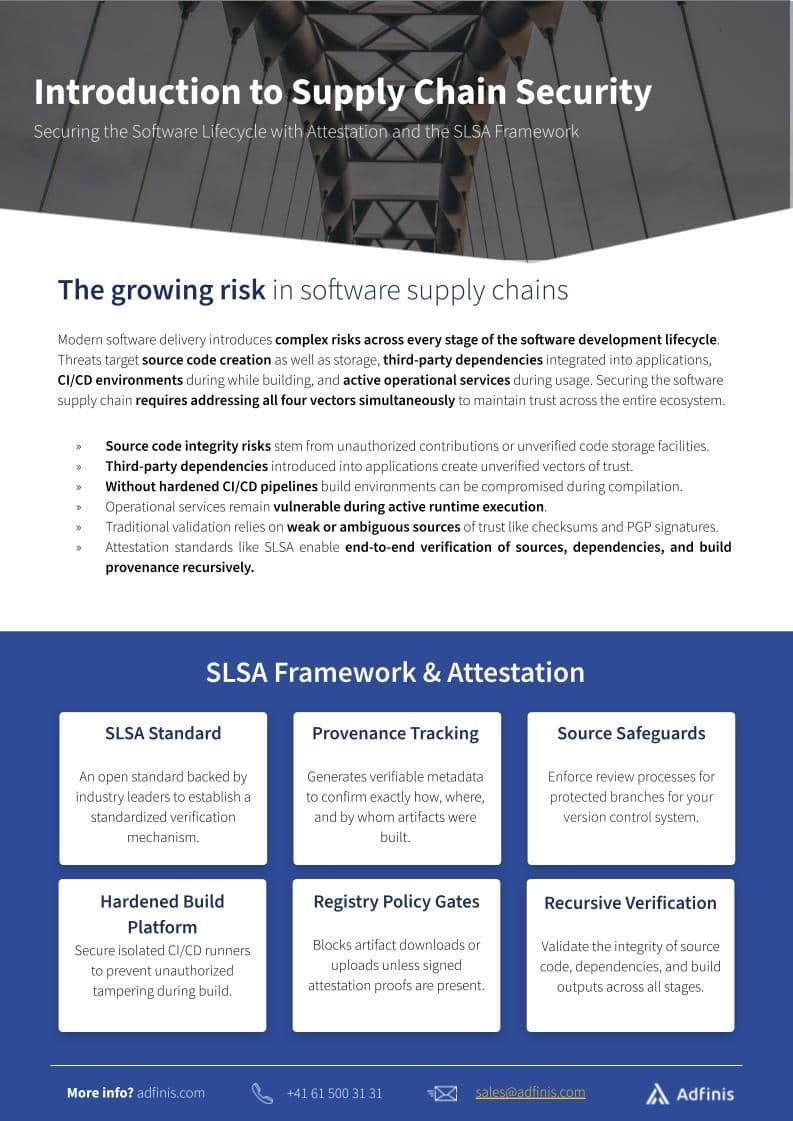
  • Learn how the Supply-chain Levels for Software Artifacts (SLSA) open standard establishes standardized verification mechanisms across development stages.
  • Discover techniques for generating verifiable metadata to track exactly how, where, and by whom build artifacts were created. CI/CD Hardening & Policy Gates: Explore practical ways to secure isolated build runners and enforce registry policy gates that block un-attested downloads or uploads.
  • Learn how Adfinis helps organizations run DevSecOps assessments and configure automated pipeline hardening.
Sign Up Now

Event Details

  • November 19, 2026

  • 11:00 – 12:00 CEST

  • Online

Sign Up Now

Introduction to Supply Chain Security

Download our 2-pager before the session to get a head start on the core principles. This quick guide breaks down the SLSA framework, source safeguards, and provenance tracking, giving you the perfect background context as Lukas Grossar expands on real-world implementation strategies during the webinar.

Download